Advanced threat detection, real-time monitoring and automated response, delivered as one fully managed service. Our 24/7 SOC protects your endpoints, networks, clouds and data centers, so your team can stop chasing alerts.
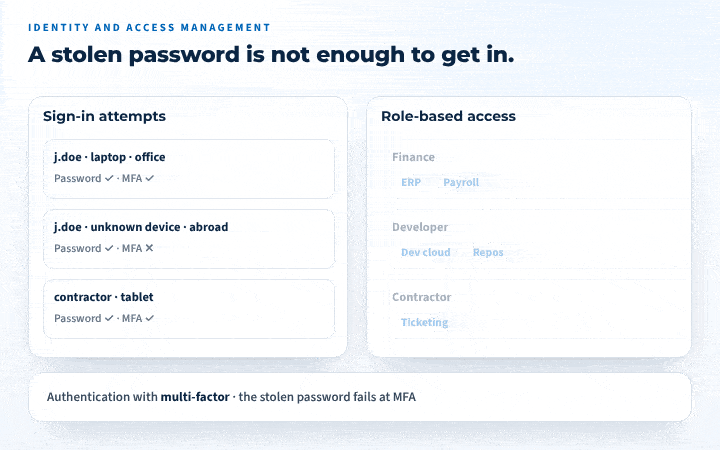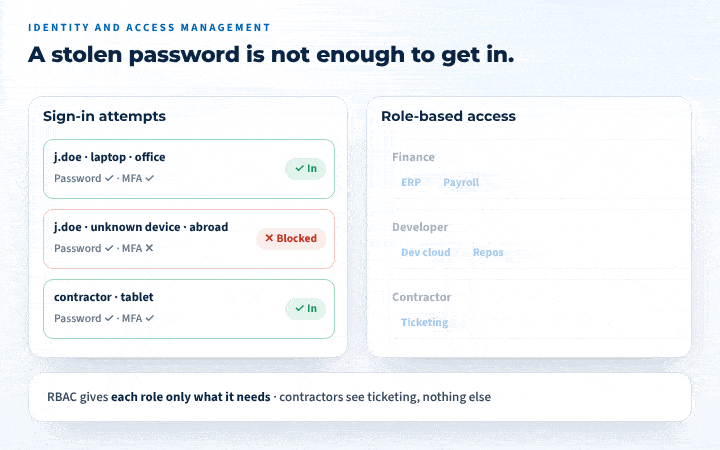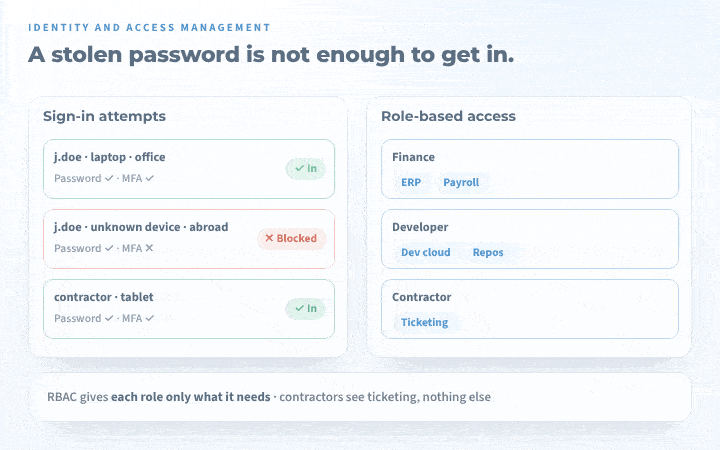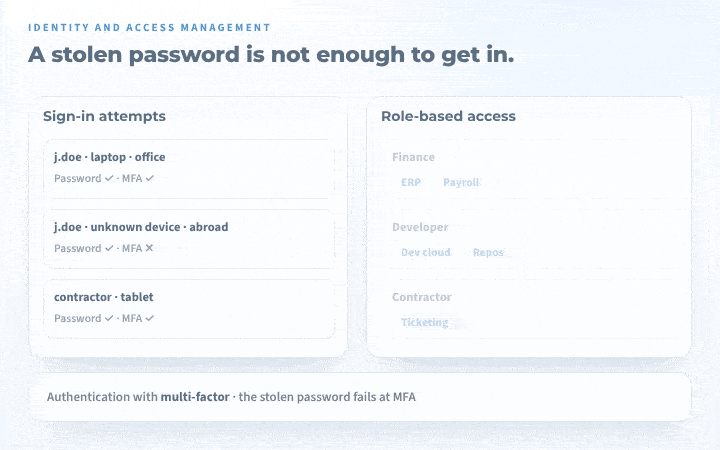
Each service works on its own; together they cover how attacks actually happen, from the first stolen password to recovery.
Advanced threat detection and prevention
AI-driven security analytics and real-time monitoring find threats early and stop them before they spread.
AI-driven analytics
Real-time monitoring
Prevention, not just alerts
DetectIsolateRestoreClose
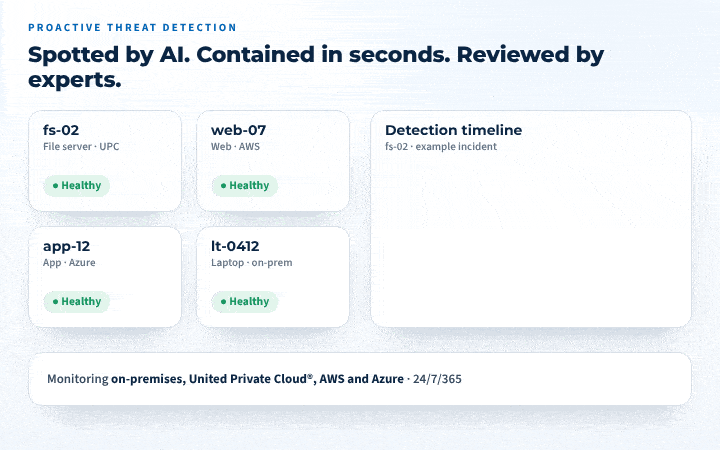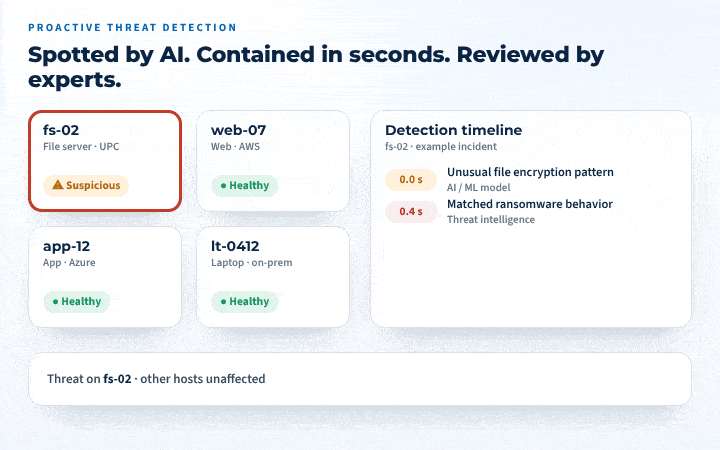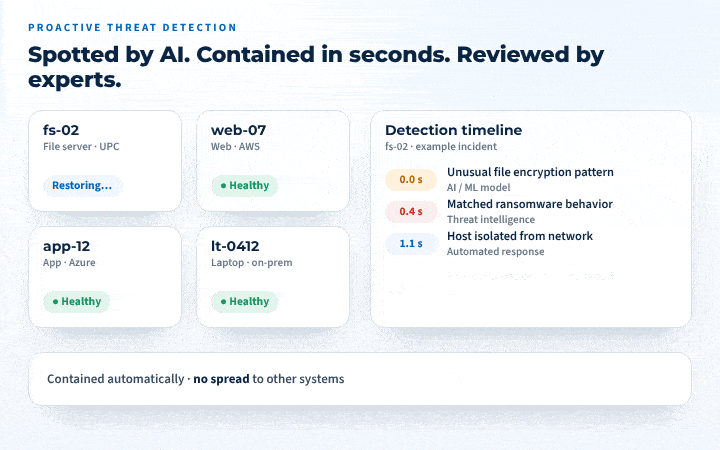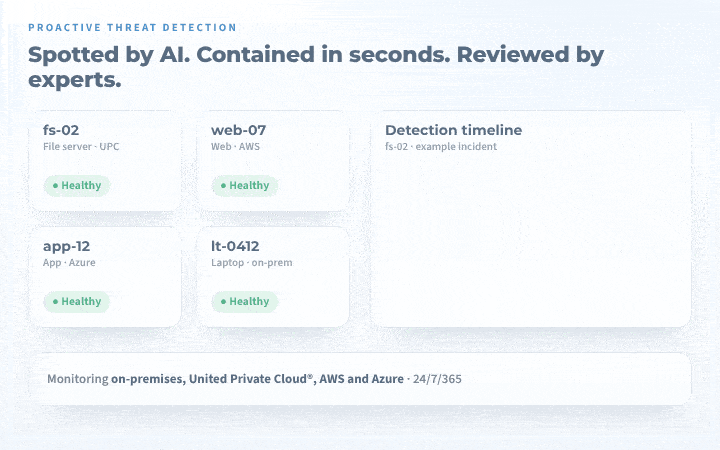
Ransomware-like behavior isolated in seconds · example
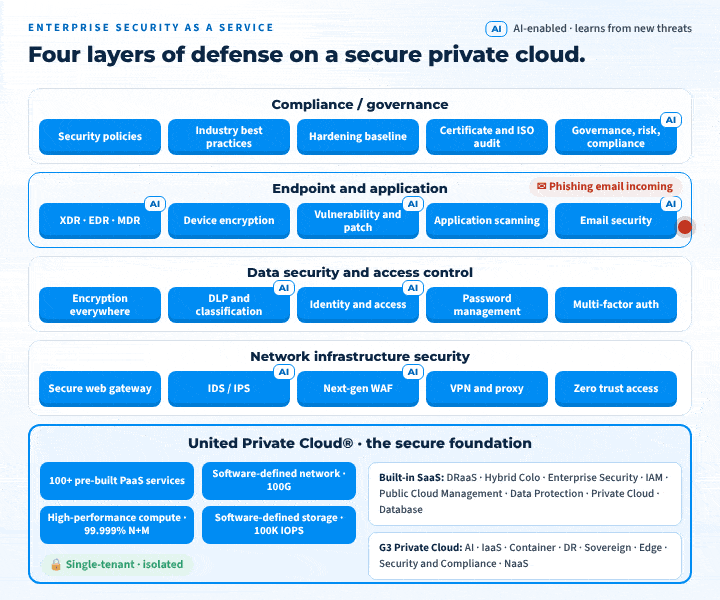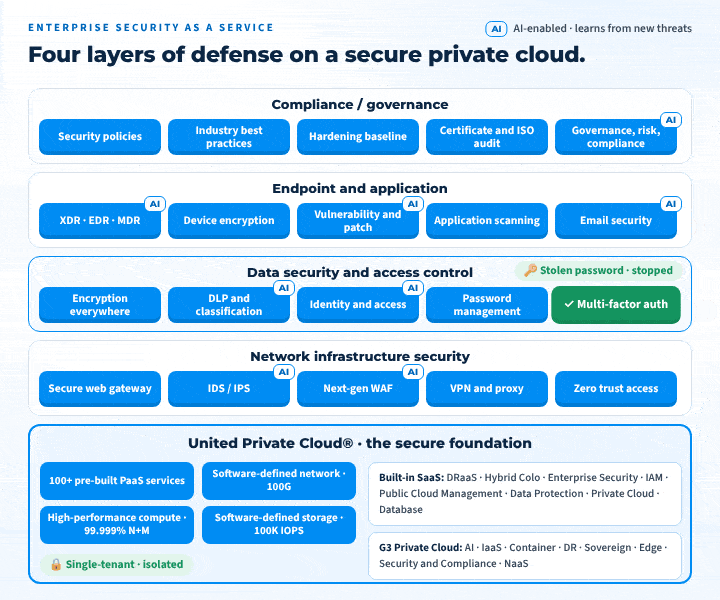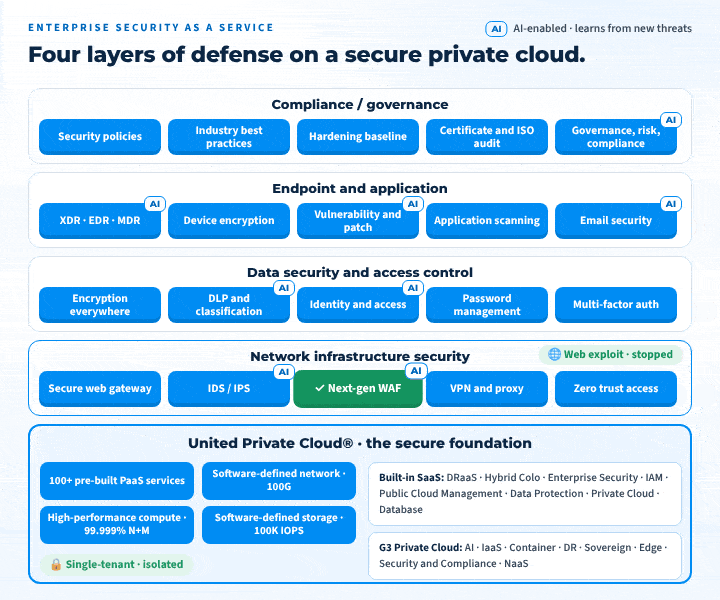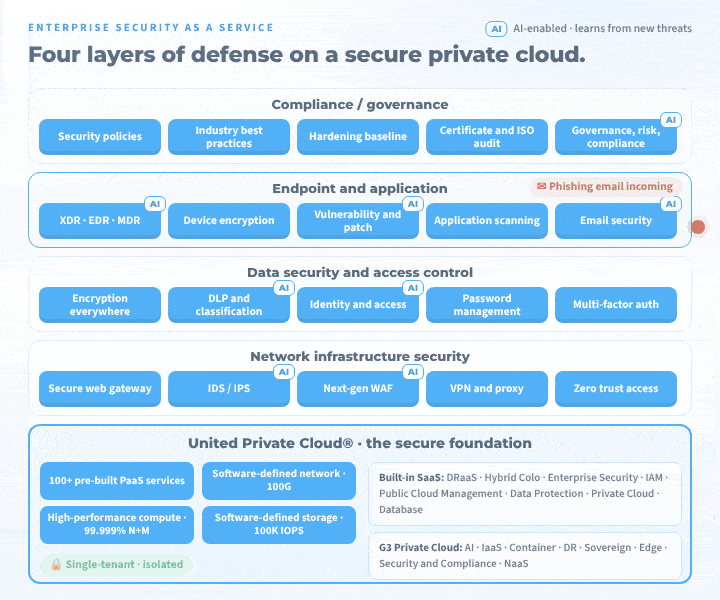
Defense in depth
Four layers of security on a secure private cloud
Every attack has to get past more than one layer. Pick an attack to see which controls stop it, and which ones stand ready behind them.
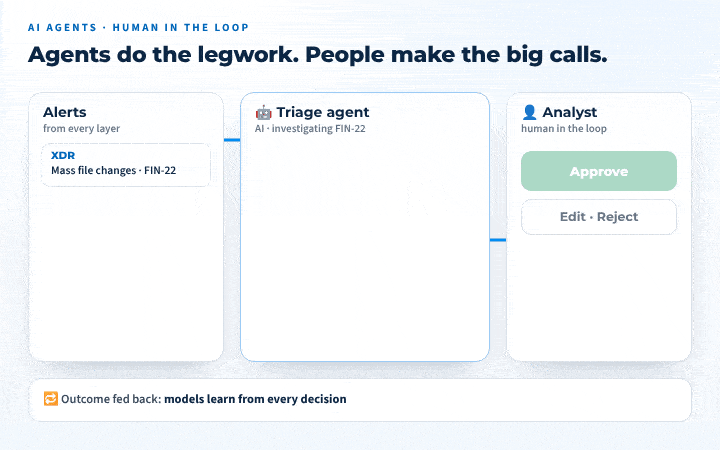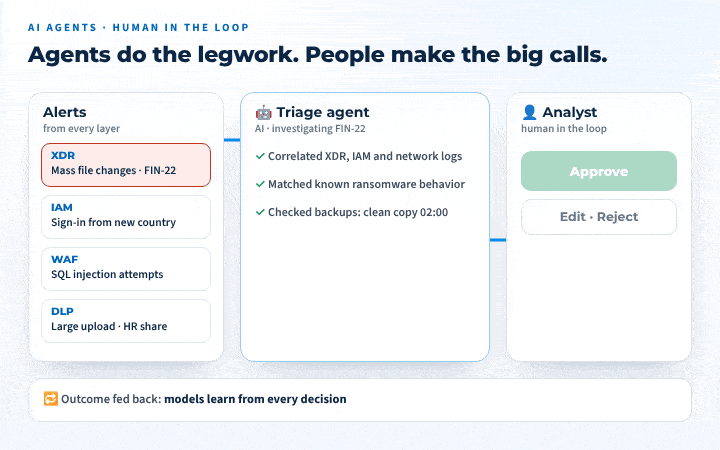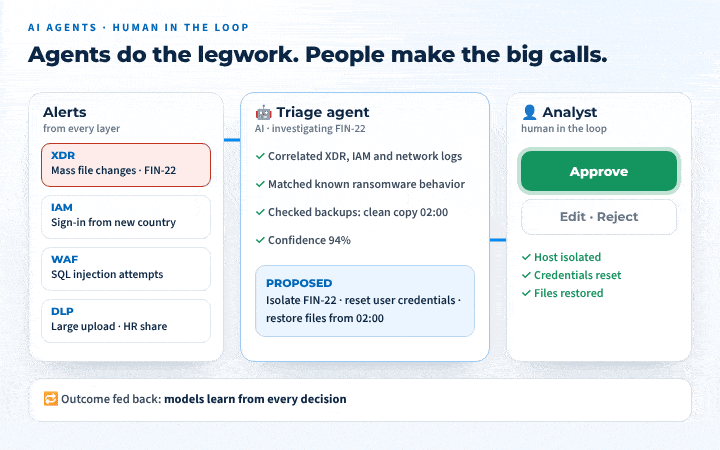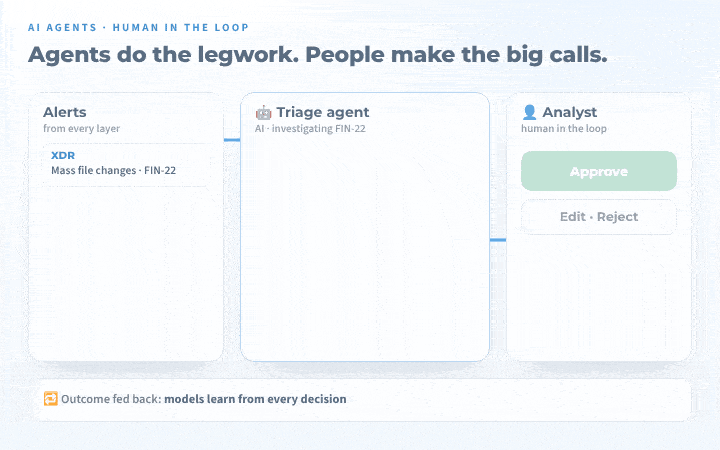
AI agents · human in the loop
Security that gets smarter every year, with people in charge
AI runs through every layer: it spots threats, investigates alerts and proposes the fix. Analysts approve the big calls, and every decision and incident teaches the models something new.
Agent queueLearning cycles: 1,284
🤖
Triage agent
Investigates every alert across all layers and proposes a fix.
🔎
Threat-hunting agent
Searches logs for attackers who slipped past the first line.
✉
Phishing agent
Finds look-alike emails and pulls them from every inbox.
🔑
Identity agent
Spots risky sign-ins and stops account takeovers.
🩹
Vulnerability agent
Ranks patches by real risk, so the worst gaps close first.
📋
Compliance agent
Catches drift from your hardening baseline and policies.
Learns from every incident
Each attack, false alarm and fix becomes training data, so detections sharpen over time.
Learns from your analysts
Every approve, edit or reject teaches the agents what your team expects.
Learns from the world
Threat intelligence keeps models current as new attack methods appear.
Stays under control
Policies set what agents may do alone and what needs a person to approve.
Why private cloud is safer
Security built into the platform, not bolted on
United Private Cloud® is single-tenant, with identity, ransomware protection, encryption and recovery built in. Pick one to see it in action.
Your cloud is yours alone
United Private Cloud® is single-tenant, so your workloads never share hardware or networks with other customers.
No noisy or risky neighbors
Clear security boundary
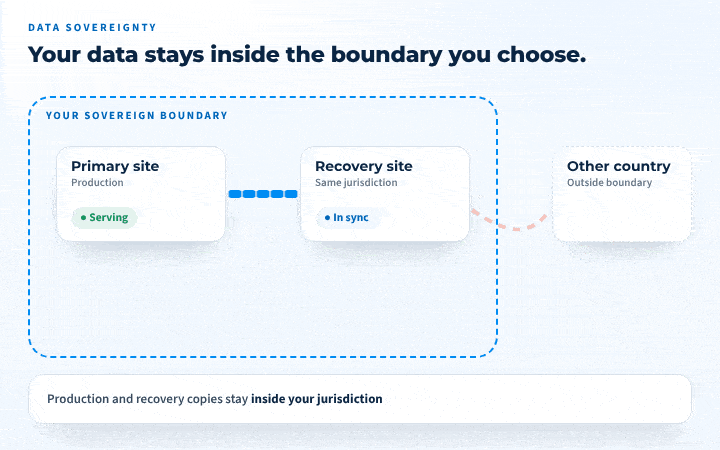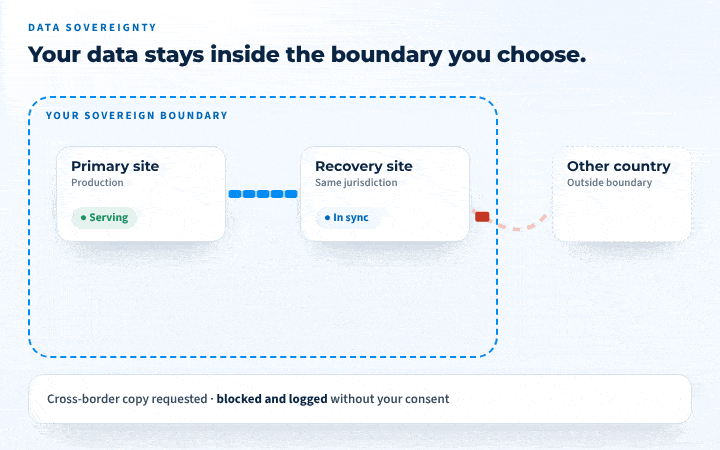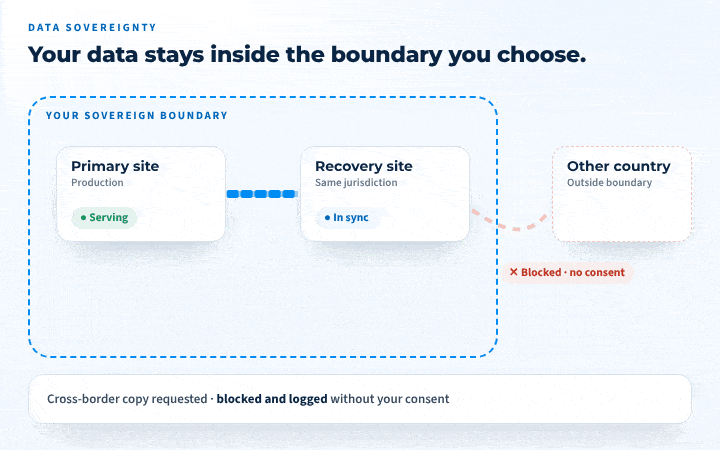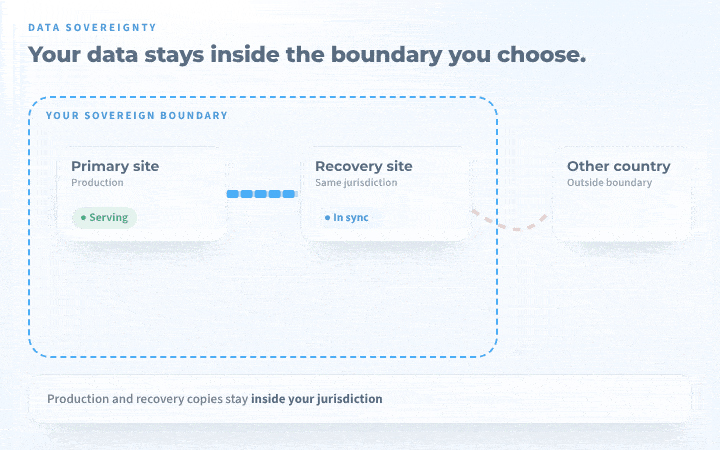
Your data stays where you choose
Single-tenantIsolatedSovereign
100+Pre-built PaaS services
100GSoftware-defined network
99.999%High-performance compute with N+M
100KIOPS software-defined storage
See it in motion
Watch the SOC at work
Seven moments from a day under Enterprise Security as a Service, from millions of logs to a clean recovery.
LIVE · AUTO-PLAYING
Coverage map
Where are you covered today?
Pick the environments you run and the protections you already have. The map shows your gaps, and what changes with Enterprise Security as a Service.
Environments you run
Protections you already have, fully staffed
COVERAGE TODAY0%
CoveredGapNot in your estate or not applicable
A self-assessment to start the conversation, not an audit. Our security team maps your real coverage in the assessment.
How it works
From exposed to watched in five steps
We map your environments, current tools, identities, data and the regulations you follow.
OUTCOMEA clear risk picture
Why UnitedLayer
Security that scales with you
Fully managed
Hand over security operations
Our experts run detection, response and compliance so your team can focus on the business.
Scalable and cost-effective
Grow without new hires
Coverage scales with your business while costs stay optimized.
Comprehensive
Endpoints to data centers
Endpoints, networks, cloud environments and data centers, protected together.
Integrated
Built into United Private Cloud®
Hybrid and multi-cloud infrastructure secured from the platform up.
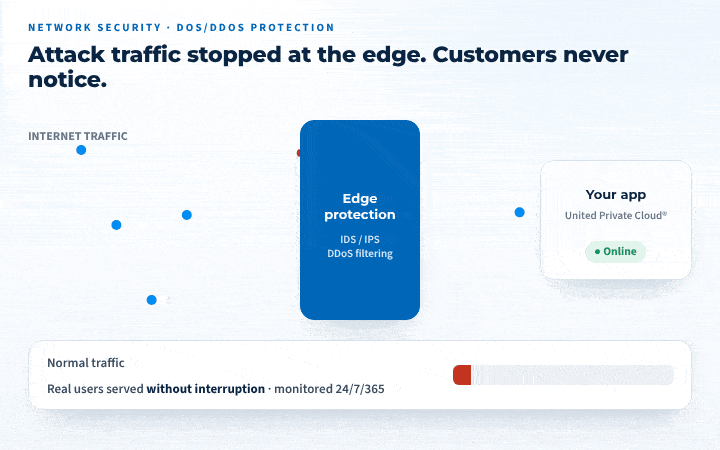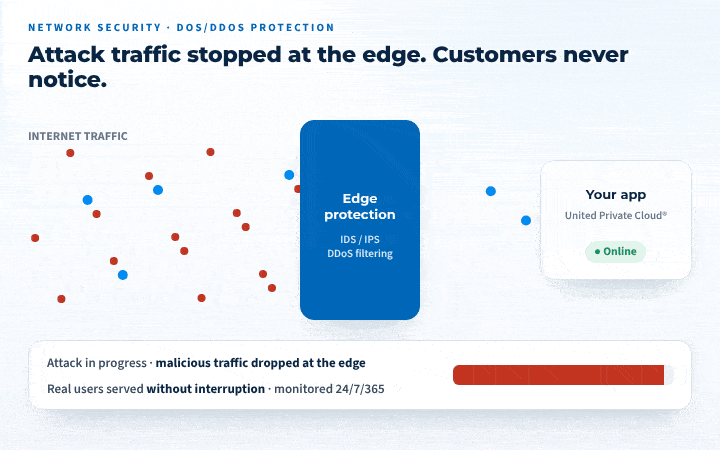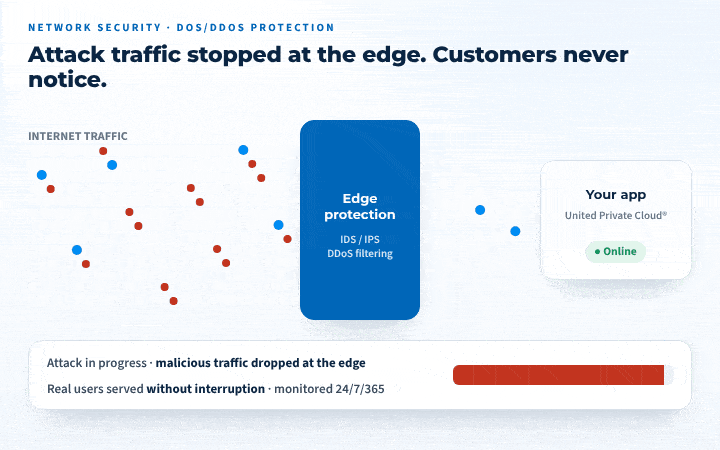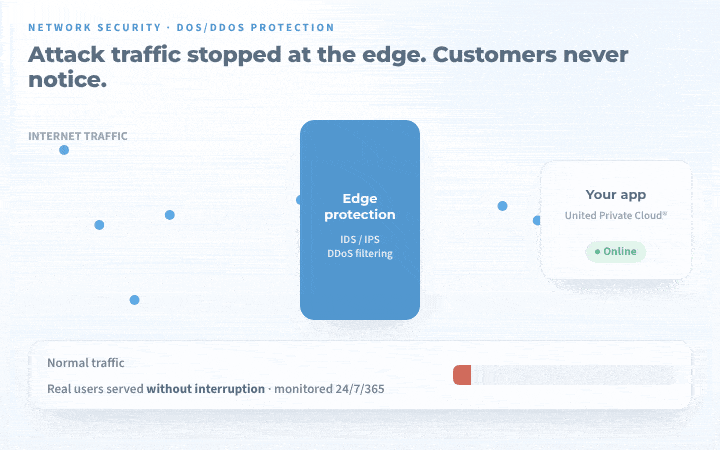
Managed next-gen firewalls, IDS/IPS and DDoS protection
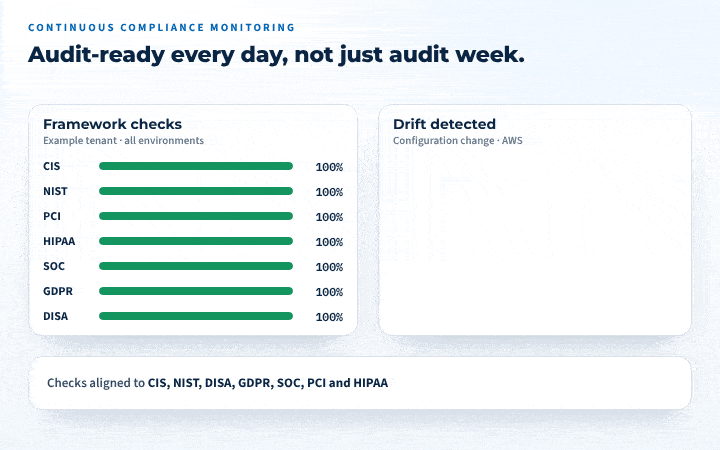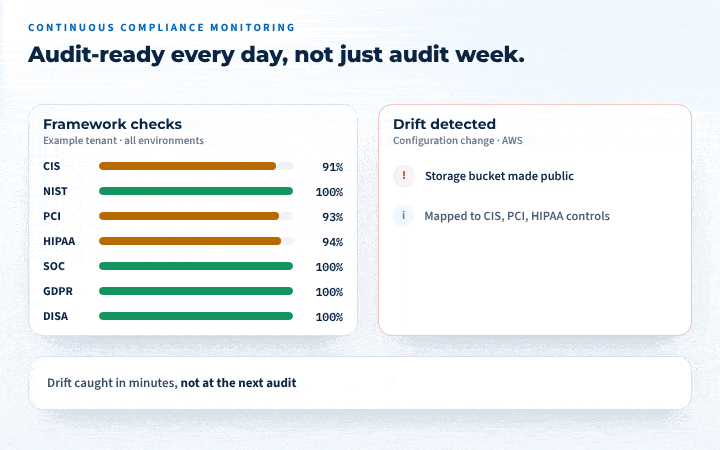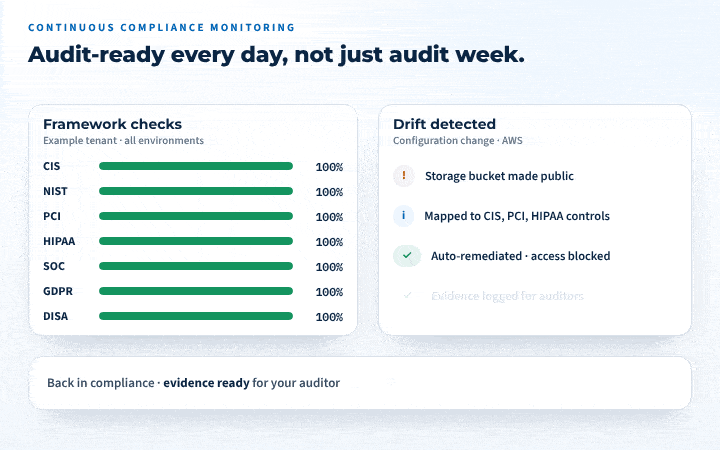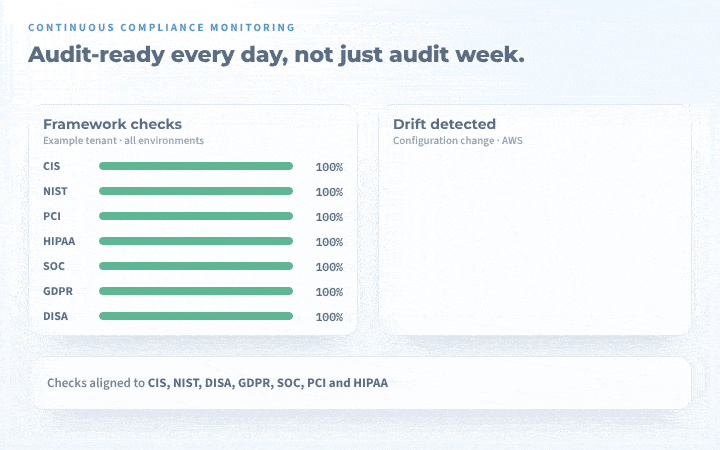
Compliance
Evidence gathered by hand
Partial reports
HIPAA, GDPR, PCI DSS and SOC 2 support
Recovery
Plan on paper
Backups only
Disaster recovery and business continuity
Questions
What teams ask before they start
What does Enterprise Security as a Service include?
Advanced threat detection and prevention, identity and access management, data encryption and loss prevention, SIEM, compliance support, managed firewalls and intrusion prevention, disaster recovery, and 24/7 SOC monitoring with expert support.
Is the SOC really staffed around the clock?
Yes. Security analysts monitor your environment 24/7 and act on threats proactively, with automated response for the events that cannot wait.
Is the SOC really staffed around the clock?
Yes. Security analysts monitor your environment 24/7 and act on threats proactively, with automated response for the events that cannot wait.
What does the SIEM do for us?
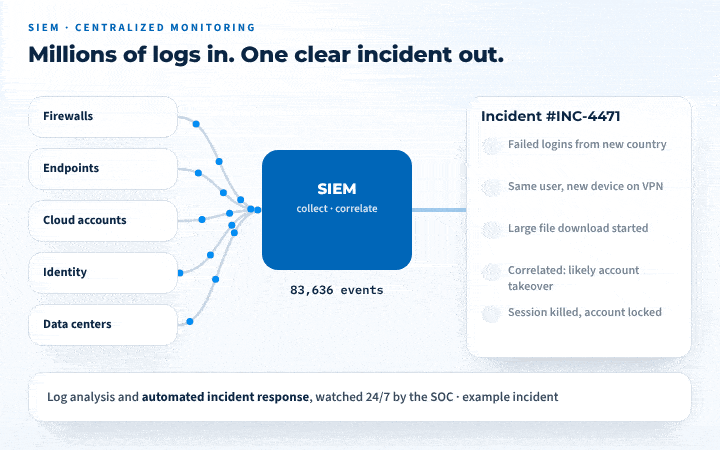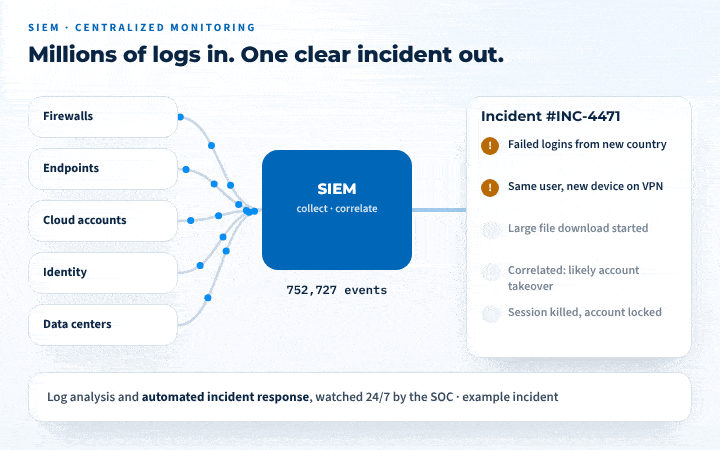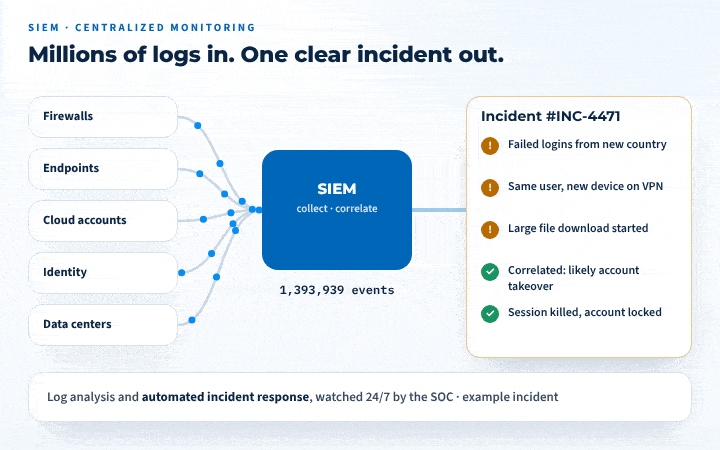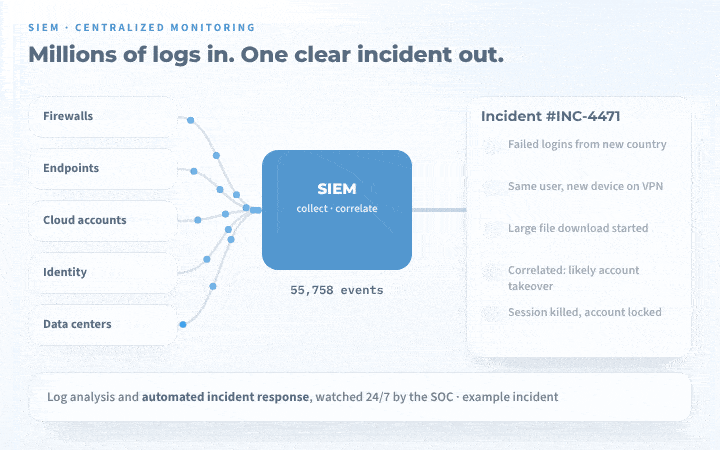
It collects logs from your firewalls, endpoints, clouds, identity systems and data centers, correlates them into clear incidents, and triggers automated response.
Which compliance frameworks do you support?
HIPAA, GDPR, PCI DSS and SOC 2, with security controls and reporting aligned to each.
Does it cover our public cloud too?
Yes. Protection spans endpoints, networks, cloud environments and data centers, and it is integrated with United Private Cloud® for hybrid and multi-cloud estates.
What happens after an attack?
Incident response contains it, and disaster recovery and business continuity services restore data and systems quickly.